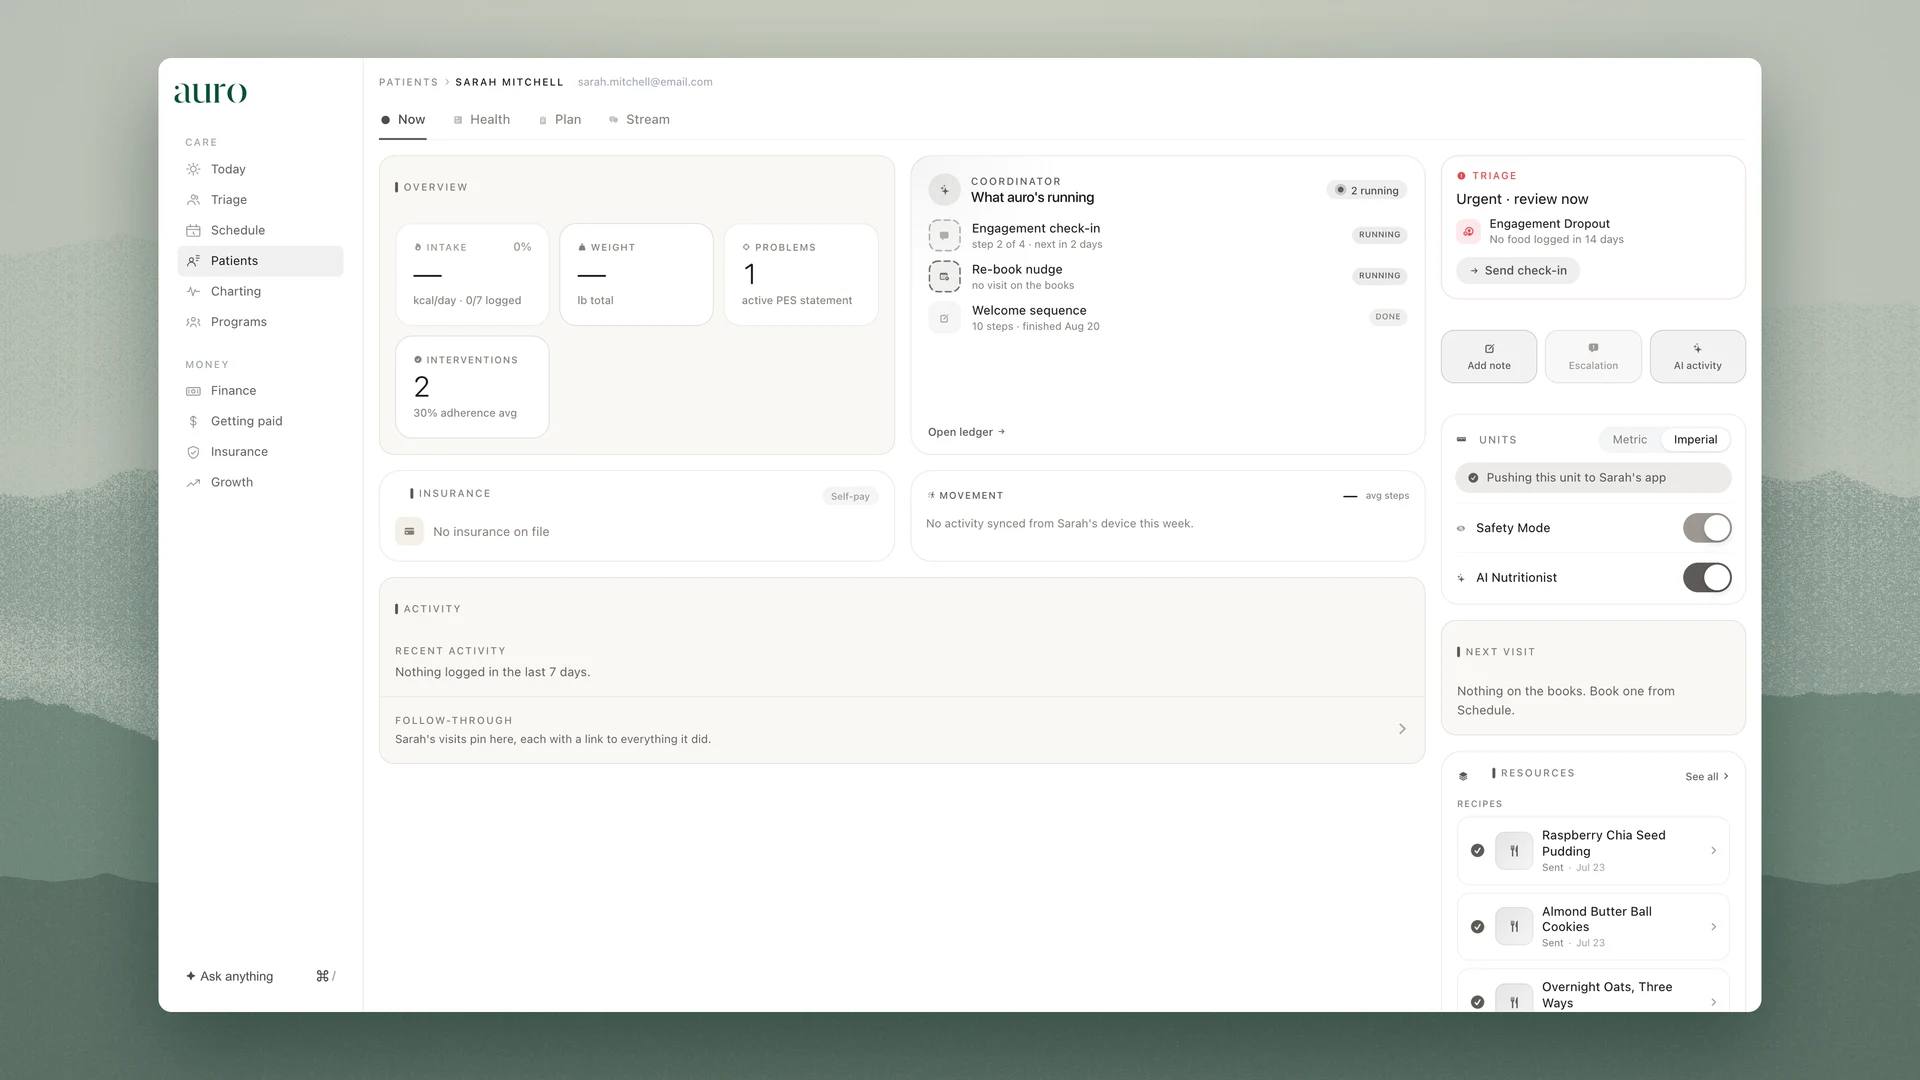
Every user is a role: owner, lead dietitian, clinician, coordinator, patient. The record shows each role only what its work needs.
Where it happens
Settings, in Trust. This lesson is part of the For the whole practice track.
What this lesson covers
Step 1
Read the five roles
Owner, lead dietitian, clinician, coordinator and patient, and what each one exists to do.
Step 2
See where the rule lives
The database enforces the role, not the screen, so a page cannot show what a role is not allowed to read.
Step 3
Multi-factor authentication, on every provider account
Every provider signs in with a second factor, and sessions expire.
Step 4
Change a role, and find the change
A permission change is an event in the audit log like any other, with a name and a time against it.
After this lesson
You can say what each role can see, and why the screen is not the thing protecting it.
The Academy keeps a record of what each person has completed. It is a record, not a credential: auro accredits no one, and no lesson carries CE or CEU credit.